php漏洞补丁已经 发布
214
- camor4天前

php.net
Security advisory: Critical remote code execution vulnerabilities, update now -...
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately. | PHP is a popular general-purpose scripting language that...
忘了说了,官方说22点,实际补丁提前十几分钟就出来了
主楼 - dalang4天前
我去,7.x的咋修复呀。
- 竹凌4天前
只能交给astra大人了,公司6千块买的小程序后台是PHP做的,我们自己又魔改了不少^-^
午时已到,我将化身天才黑客!
- yukinoi4天前
这是世界上最好的大逃杀游戏
- 陈寒彤4天前
- lan4天前
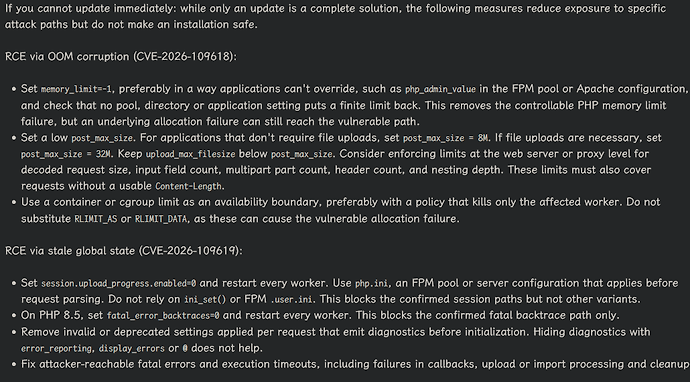
停止维护了,好像有临时抢救方法。
- dalang4天前
事已至此,明天肯定有7.x的修复方法,明天再说吧
- Inex_zero4天前

github.com
GitHub - php/php-src at PHP-7.4-CVE-2026-109618-109619
PHP-7.4-CVE-2026-109618-109619
The PHP Interpreter. Contribute to php/php-src development by creating an account on GitHub.
看源码修呗(
- Xinalin4天前
- everyback4天前
完蛋喽,关session治不好,只有关multipart才有用,一大批不老不新的php站点要完蛋了,官方不把旧版本官方fix发出来基本上就是在拆php老站点的根了
- Cland4天前
一是修改
php.ini配置文件,添加或调整以下配置项,关闭会话上传进度功能并开启严格模式:```
session.upload_progress.enabled = 0
session.use_strict_mode = 1
```修改完成后重启PHP-FPM或对应Web服务,确认配置生效。二是通过WAF、反向代理等边缘程序,收紧
multipart/form-data类型POST请求的检测规则,对无需文件上传的业务端点限制或拦截上传请求,收缩攻击面。 - SomeBottle4天前
在低版本 PHP 补丁出来前可以直接先禁止所有 multipart 请求,比如 nginx 的:```
server {
# 其他现有配置...if ($http_content_type ~ "^\smultipart/") {
return 415;
}# ...
} - Cland4天前
- qwer32344天前
旧项目有不少都是7.4版本,这下完犊子了 ^-^